Topics Discussed
You can use this document to send Fortinet Security Gateway logs to Armor's Security Information & Event Management (SIEM).
Pre-Deployment Considerations
Before you begin, review the following requirements:
Log Relay
To create a remote Log Relay, you must already have:
-
A Log Relay server on your account
-
To learn how to add Log Relay to your account, see Obtain Log Relay for Remote Log Collection
-
-
Configured the system clock
Log Relay IP Address
You must be able to retrieve the log relay IP address from your Nexus account:
-
In Nexus, on the left nav, hover-over Threat Management

-
Click Log Search.
-
Then Agent Sources.
-
Locate and select the desired log relay.
-
Click Overview.
-
Locate and copy the Public IP.
Update your Fortinet Security Gateway
-
Log into your Fortinet Security Gateway.
-
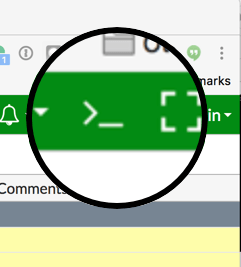
In the upper, right corner, select CLI Console.
-
Run the following commands to configure the device to send syslogs to Log Relay, which will then forward the logs to Armor.
Bashfgvm1 # config log syslogd setting fgvm1 (setting) # set status enable fgvm1 (setting) # set format default fgvm1 (setting) # set server <LOG_RELAY_IP_ADDRESS> fgvm1 (setting) # set port 10073 fgvm1 (setting) # end-
To validate your current configuration, run the following command, either before or after the [fgvm1 (setting) # end] command.
Bashfgvm1 # show log syslogd settingIf the format was set to something other than default, when the [fgvm1#show log syslogd setting] command is run, the current format will be returned (e.g. cef).
Within the command line, update the format command to default [fgvm1 (setting)#set format default].
-
-
Verify that logs are formatted correctly, similar to either of the following examples:
Fortigate can send messages in multiple formats.
Example 1
Jul 9 14:26:58 13.47.22.124 date=2019-07-09 time=14:26:58 devname=XXX-FW1 devid=YYY logid=0000000013 type=traffic subtype=forward level=notice vd=root srcip=89.28.174.28 srcport=46796 srcintf="port9" dstip=13.47.22.175 dstport=1639 dstintf="port11" sessionid=2232272452 proto=6 action=deny policyid=0 policytype=policyExample 2
date=2019-07-09 time=14:26:58 devname=XXX-FW1 devid=YYY logid=0000000013 type=traffic subtype=forward level=notice vd=root srcip=89.28.174.28 srcport=46796 srcintf="port9" dstip=13.47.22.175 dstport=1639 dstintf="port11" sessionid=2232272452 proto=6 action=deny policyid=0 policytype=policy
Verify Logs
-
In Nexus, hover over Threat Management
-
Click Log Search.
-
Then click Log Search tab on the top of the page.
-
Wait for the SSO.
-
-
In the search field, enter the IP address or the device name.
-
For example, you can enter *13.47.22.124* or *XXX-FW1*
-
This action will display collected FortiGate logs for that particular device.
-
Troubleshooting
Command Help
Within the CLI Console, you can use the question mark (?) key to display command help.
-
To display a list of available commands, press the question mark (?) key.
-
A list of the available commands will display, along with a description of each command.
-
-
To display a list of the options available for that command, type a command, followed by a space, then press the question mark (?) key.
-
A list of the options available for that command will display, along with a description of each option.
-
-
To display a list of additional options available for that command option combination, type a command, followed by an option, then press the question mark (?).
-
A list of additional options available for that command option combination will display, along with a description of each option.
Example Output
show system interface ?
-
Additional Documentation
For more information on using CLI, click here.